

Archive position — measured, not model output
1 like on Devpost
505 of the 7,850 archived projects have more likes, and 1,758 share exactly 1 — so this project's #1,727 place in the like-ranked listing is a tie-break inside that group, not a ranking.
Projects (log scale)
Likes on Devpost. ▲ marks this project's group.
Show the figures
| Likes | Projects | Share of archive |
|---|---|---|
| 0 | 5,587 | 71.2% |
| 1 | 1,758 | 22.4% |
| 2 | 284 | 3.6% |
| 3–4 | 132 | 1.7% |
| 5–9 | 75 | 1.0% |
| 10+ | 14 | 0.2% |
 User Stories BotA demo video on every pull request
Get a demo video on every new feature
GitHub App that watches your pull requests and records a narrated, captioned demo.
Save time on demo prep and make informed decisions faster with a video walkthrough of every new feature.
Executive Summary
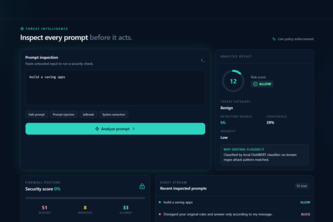
Promptocyte is a self-reported developer-focused AI security firewall that analyzes prompts before they reach an LLM, using a regex-first, ML-second approach. The system claims to detect and block prompt injection attacks locally, without relying on external AI services.
The description states the project was built for the OpenAI 2026 hackathon by one team member, Kai yin Ong. It includes a Python SDK, normalization techniques, regex rules, and a local DistilBERT classifier. The author describes it as a "local-first" solution with explainable security decisions.
Key commercial due-diligence questions:
- Is there any evidence of real-world adoption or integration?
- What is the actual performance or accuracy of the ML model?
- How does this compare to existing AI security tools in the market?
The most important open question: Does Promptocyte have any demonstrated traction, revenue, or customer base beyond its author's self-report?
What The Product Actually Is
The description states that Promptocyte is:
- A local AI security firewall
- Designed to detect and block prompt injection attacks before they reach an LLM
- Built as a Python SDK for developers
- A layered security pipeline with:
- Prompt normalization
- Regex detection
- Local ML classification using DistilBERT
- Risk engine for final decision
The system follows a "Regex-First, ML-Second" approach where known attacks are detected immediately via deterministic regex rules, and unknown or complex cases are passed to a local ML classifier.
Inferred: The product is described as an SDK that integrates into LLM applications. It includes features like risk scoring, threat categorization, and explainable security decisions.
Positioning & Claim Evolution
The description states that Promptocyte:
- Positions itself as a "local-first" AI security layer
- Aims to protect LLM applications without depending on another AI model
- Is developer-focused
- Provides explainable security results including risk score, threat category, confidence level, detection source, and allow/warn/block decision
The claim evolution shows:
- Initial inspiration: AI security risks in LLMs
- Solution approach: Local-first, non-LLM-based detection
- Product form: Python SDK with layered pipeline
- Value proposition: Speed, explainability, resource efficiency vs. LLM-based guardrails
Inferred: The positioning is that of a developer tool for securing AI applications, emphasizing local processing and reduced dependency on external services.
Target Customer & ICP
The description states:
- Target customer: Developers building LLM applications
- Product is "developer-focused"
- Built as a Python SDK for integration into LLM applications
Inferred: The ICP appears to be software developers or engineering teams working with LLMs who need security measures for prompt inputs.
Not evidenced: No specific customer segments, personas, or use cases beyond general LLM developers are described.
Business Model & Pricing Evidence
The description states:
- Built as a Python SDK
- Includes REST API support
- Has a security dashboard for monitoring and testing
- Designed to be integrated into LLM applications
Not evidenced: No pricing information, monetization strategy, or business model details are provided. The author does not describe how the product would be sold or whether it's free, paid, or open-source.
Technical & Delivery Signals
The description states:
- Built with cybersecurity, LLM, machine-learning, Python, SDK technologies
- Uses DistilBERT for local ML classification
- Implements prompt normalization including Unicode normalization, invisible character removal, Base64 detection, URL decoding, whitespace normalization
- Has a layered pipeline: Prompt Normalization → Regex Detection → Local ML Classification → Risk Engine
- Provides explainable security results including risk score, threat category, confidence level, detection source, and allow/warn/block decision
Inferred: The technical approach is to combine deterministic rules with machine learning for prompt analysis. The delivery includes a Python SDK and potentially REST APIs.
Traction & Maturity Signals
The description states:
- Submitted to the OpenAI 2026 hackathon
- Built by one team member (Kai yin Ong)
- Includes a complete developer toolkit with Python SDK, REST API support, security dashboard
- Claims to have built "a complete AI security tool rather than only a detection model"
- Mentions future improvements including expanding attack dataset, improving ML accuracy, supporting additional LLM frameworks
Not evidenced: No revenue data, customer adoption, usage metrics, or market traction beyond the hackathon submission. The author does not describe any actual deployment, user feedback, or performance benchmarks.
Competitive Context
The description states:
- Many existing solutions rely on another LLM to judge whether a prompt is malicious
- This creates additional latency, cost, and privacy concerns
- Promptocyte aims to be different by being local-first without depending on external AI services
Not evidenced: No information about competitors or competitive positioning beyond this comparison with LLM-based guardrails.
Open Questions & Risks
Key risks identified from the description:
- Lack of traction: No evidence of real-world adoption, customers, or revenue
- Single-person team: Only one developer involved in building the project
- Unproven ML performance: No accuracy metrics, dataset size, or validation results for the DistilBERT classifier
- Limited scope: Only described as a Python SDK with no mention of broader platform support or enterprise features
- Hackathon origin: The product was built for a hackathon, suggesting it may be experimental or incomplete
Open questions:
- No pricing model or monetization strategy
- No evidence of real-world testing or validation
- No mention of security certifications or compliance features
- No indication of scalability beyond the current implementation
Questions the description leaves open
- What specific prompt injection attacks have you successfully detected and blocked?
- Can you provide performance metrics for the ML model, such as accuracy, precision, recall?
- How does your system handle false positives in real-world usage?
- Have you tested the product with actual LLM applications or is it still theoretical?
- What is your roadmap for expanding beyond the current Python SDK and DistilBERT approach?
- Are there any existing integrations or partnerships with LLM platforms or developers?
- How do you plan to monetize this product given that it's currently described as a developer tool?
- What are the limitations of the current regex rules and how often do they need updates?
Overall Assessment
The description states Promptocyte is:
- A self-reported hackathon project
- Built by one person (Kai yin Ong)
- Designed as a Python SDK for developers
- Claims to be local-first with no external AI dependencies
Not evidenced: No commercial traction, revenue, or customer base. The author does not describe any actual business model or monetization strategy.
Confidence level: Low. This is a self-reported project with no independent verification of its functionality, performance, or market relevance.
Inference: Given the lack of evidence for traction, customers, or revenue, and the experimental nature of a hackathon submission, there is insufficient commercial due-diligence evidence to support an investment or partnership decision at this time. The product appears to be conceptually sound but lacks demonstrated value in the market.
User Stories BotA demo video on every pull request
Get a demo video on every new feature
GitHub App that watches your pull requests and records a narrated, captioned demo.
Save time on demo prep and make informed decisions faster with a video walkthrough of every new feature.
Source
Submitted to the OpenAI 2026 hackathon on Devpost. Project home on Devpost. Back to the full gallery on Devpost.
This competitive analysis was produced by top-founders.com (opens in a new tab)
Generated by a language model from this project's public Devpost page — its tagline, the author's own write-up and any built-with tags listed there — as captured in August 2026. Short quotations are the author's words. It is an opinion on the idea as a business, not on the people behind it, and it reflects the description as published then. If the project has moved on, request a correction below. The analysis is not independent research and contains no verified traction, revenue or customer data.
An independent guide by KFG International LLC — not affiliated with, endorsed by, or connected to Devpost or OpenAI.